Block App Internet Access on Mac
Learn when to block a Mac app, how to avoid breaking expected workflows, and how local firewall rules help keep the decision precise.
Read: Block App Internet Access on MacUnderstand outbound connection control on macOS and how to pair app traffic visibility with local rules for apps, domains, IPs, ports, and protocols.
Written by iNTM · Content updated:
The built-in macOS firewall focuses mainly on inbound access. For outbound connection control, you need app-level visibility and rules that can target applications, domains, IP addresses, ports, or protocols. iNTM combines outbound traffic monitoring with local firewall control.
Open iNTM Firewall > Realtime and select the app making the outbound connection; the app list gives more context than an interface total.
Check the domain, IP address, port, protocol, and connection timing.
Compare with app behavior, traffic history, and your own workflow.
Choose a block or allow action for the selected connection, check the app and target in the rule sheet, then review the saved rule in Firewall > Rules.
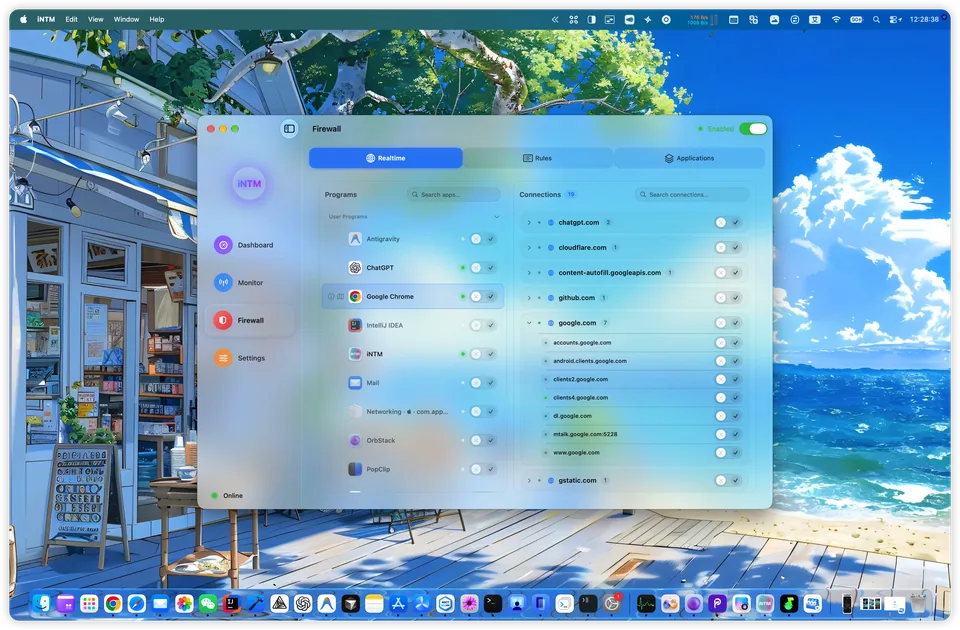
Confirm the rule reduced unwanted traffic without breaking required app features.
Inbound rules control what can connect into your Mac. Outbound rules control what your apps can reach. For privacy and bandwidth investigation, outbound visibility is often the missing piece.
A precise outbound rule combines the app identity with endpoint context. Domain rules are readable, IP and port rules can be more exact, and protocol context helps explain what type of traffic is involved.
Inbound protection addresses connections arriving at services on your Mac. Outbound control addresses destinations reached by your apps. Choose rules from the direction and target of the connection; adding outbound control does not make the built-in firewall settings irrelevant.
Apple documents the built-in macOS tools below. iNTM features are described in our product overview. Product
The built-in firewall is mainly focused on inbound connections. iNTM adds app-focused outbound visibility and local rule workflows.
Yes. iNTM supports local rules for domains as well as apps, IP addresses, ports, and protocols.
Inspection reduces false positives. Many apps need outbound access for login, sync, updates, and collaboration.
Learn when to block a Mac app, how to avoid breaking expected workflows, and how local firewall rules help keep the decision precise.
Read: Block App Internet Access on MacUnderstand traffic patterns before creating rules.
Read Monitoring Guide